
Cisco Expands AI Agent Security With Astrix and WideField Deals
Cisco is strengthening AI-driven identity security through its Astrix Security acquisition and planned WideField Security deal. The strategy enhances non-human identity governance, AI agent visibility, and session-level investigation capabilities across enterprise environments and Splunk.
SailPoint Acquires Entro Security in Reported $200 Million Deal
SailPoint has acquired Entro Security in a reported $200 million deal to strengthen machine identity protection. The acquisition expands SailPoint’s identity security platform with secrets discovery, credential monitoring, and governance for service accounts, API keys, tokens, certificates, and AI agents.
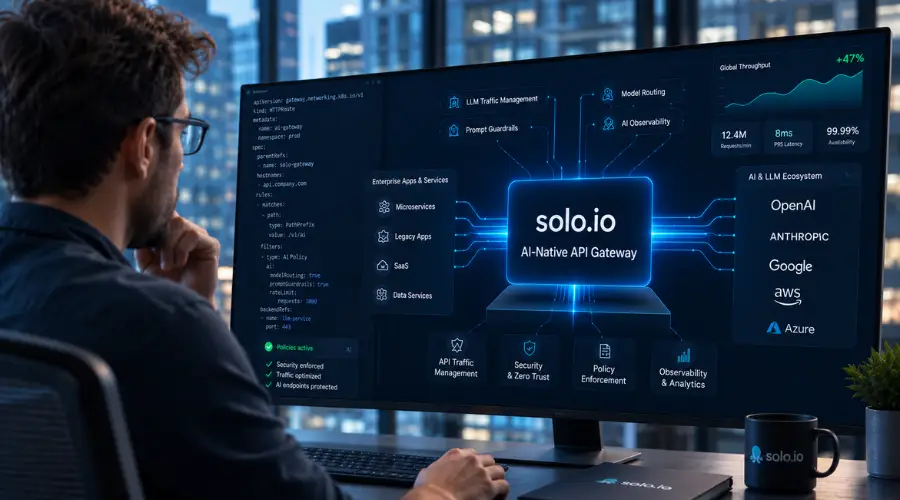
How Solo.io Is Building AI-Native API Gateways for Enterprises
As enterprises transition from basic chatbots to complex, multi-model AI workflows, traditional network routing architecture falls short. Solo.io addresses this fragmentation directly with its Gloo AI Gateway, introducing token-aware rate limiting, unified LLM API abstraction layers, and automated prompt-injection guardrails to govern AI traffic at scale.
PerfectScale’s Approach to Autonomous Kubernetes Optimization
Over-provisioning containers to prevent downtime is a broken operational strategy. Discover how PerfectScale by DoiT bridges the engineering-to-finance divide by delivering continuous, autonomous, in-place resource optimization that safeguards workload SLAs without relying on destructive pod restarts.
How Kubernetes Cost Visibility Is Becoming a FinOps Priority
A $500,000 cloud bill means nothing if you can’t track which microservices drove the spend. Discover how Kubernetes cost visibility is revolutionizing modern FinOps by breaking through cluster-level blind spots to deliver granular, workload-level cost attribution, enabling engineers to build cost-efficient architectures without sacrificing scale.
Styra and the Growing Demand for Policy-as-Code Governance
As cloud-native environments scale, manual compliance checks inevitably break down. Discover how policy-as-code closes this critical gap. This deep dive explores how Open Policy Agent (OPA), the open standard incubated by Styra, decouples decision-making from implementation to automate governance across Kubernetes clusters, CI/CD pipelines, Infrastructure-as-Code (IaC), and emerging autonomous AI systems.
How Nirmata Replaces Manual YAML with AI-Driven Policy Automation
Kubernetes policy has always promised more control, better consistency, and fewer security mistakes. Policy work often falls on platform teams that are already very busy.
A-LIGN’s Playbook for Painless Cloud Compliance
Cloud compliance has become harder to manage as companies add more cloud services, more internal tools, and more customer-driven security requirements. What used to be

How Open Logic De-Risks Enterprise Open Source at Scale
Open source software is now part of almost every modern technology environment. Companies use it for cloud infrastructure, data platforms, streaming systems, development frameworks, and

Beyond VPNs: Teleport’s Identity-First Infrastructure Access
For years, VPNs answered a straightforward question: how do engineers securely reach internal infrastructure? That answer made sense when teams worked from a single office,

How A-LIGN’s ascend platform Is making audits faster with AI
Colleen Conti, Director of Product Marketing at A-LIGN, breaks down how modern audit management actually works — from navigating SOC 2, ISO 27001, and CMMC

How Dunelm Uses CloudQuery and Snowflake to Enhance AWS Security
Dunelm is a large, UK-based home retailer specialising in furniture, homewares and DIY necessities. As well as a large estate of retail stores, the company runs a major e-commerce platform offering home delivery services as well as in-store collection. This multi-channel approach means that the…


